Posts

Setting up CUDA environment in Visual Studio 2017
Image
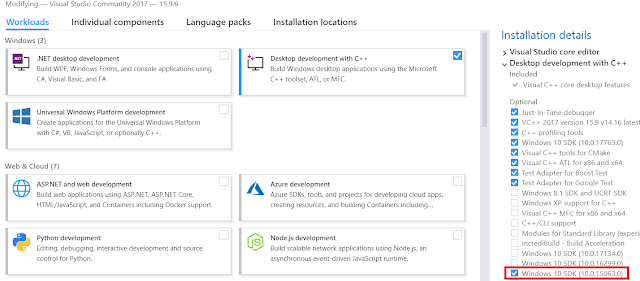
In this post I will briefly summarise two issues I came across while trying to setup the development environment for CUDA. CUDA is an environment that allows you to code the application with support of potent computational capabilities of your GPU-s. In my case, I wanted to utilise the power of NVIDIA GeForce 1050 Ti card. The idea of having this SDK is to facilitate a way for your application to distribute processing over parallel processing and multithreading. You can download CUDA SDK from  https://developer.nvidia.com/cuda-downloads . (I used 10.1 version and Visual Studio 2017). Having downloaded and installed CUDA SDK (which takes some time), I tried to compile the deviceQuery utility - the example that, if compiled ok, would show you the attributes of your GPU. This is where the troubleshooting started. First of all, the compilation did not work due to missing Microsoft 10 SDK 10.0.15063.0 component. This can be easily installed by modifications in the Visual Studio. Go in...

Attacking encrypted VOIP (SIP) protocols

Image
In this post I will be explaining the approach in attacking the encrypted voice over IP (VOIP) protocol, more specifically, SIP (Session Initiation Protocol).  When we are talking about the SIP encryption, it will most likely assume some kind of SSL/TLS wrapping (SIP over TLS). An example below shows the solution design that allows interception, decryption and manipulation of SIP messages. The central component consists of mitm_relay.py and BURP. It is not required that both BURP and mitm_relay run on the same machine, but my setup did run both of them on the same virtual instance. The communication chain looked like this: Client -> mitm_relay->BURP->SIP Server->Client 2 The mitm_relay.py is a python script available at https://github.com/jrmdev/mitm_relay Before we fire up the mitm_relay, we need to configure couple of things- its certificate (self signed in my case, and private key). Once this is in place, we can run it: Few details about the mitm_rel...

Armouring reverse_tcp to evade antivirus detection

Image
This was the presentation I held on 23rd March 2019 at the BSides Dublin 2019.

Signature verification bypass vulnerability in some Huawei routers

Image
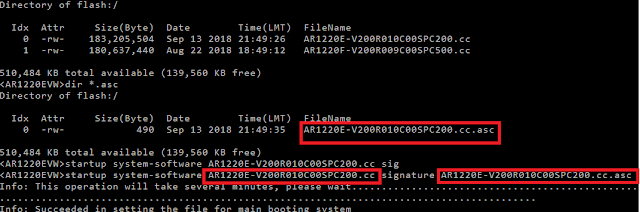
This blog will describe the discovery of the digital signature bypass on some Huawei routers.  The idea of digital signature check is simple - you have a piece of code and you calculated the checksum/hash of that file. The hash or checksum can be thought of as a "signature", a mathematical value that is uniquely assigned to the code (in our case the code was a firmware file). As soon as you change anything in the file and recalculate the hash, it should be significantly different from the original value - that is the feature of the hashing algorithm. Even the small change in the code will change the hash significantly. Vendors in most cases provide the such a pre-calculated hash so that the customer or the system may check if the hash of the image is indeed the same as vendor required. What was found in this investigation was that the system command on the Huawei AR1220E router does not perform this check properly. As a consequence, the attacker might be abl...